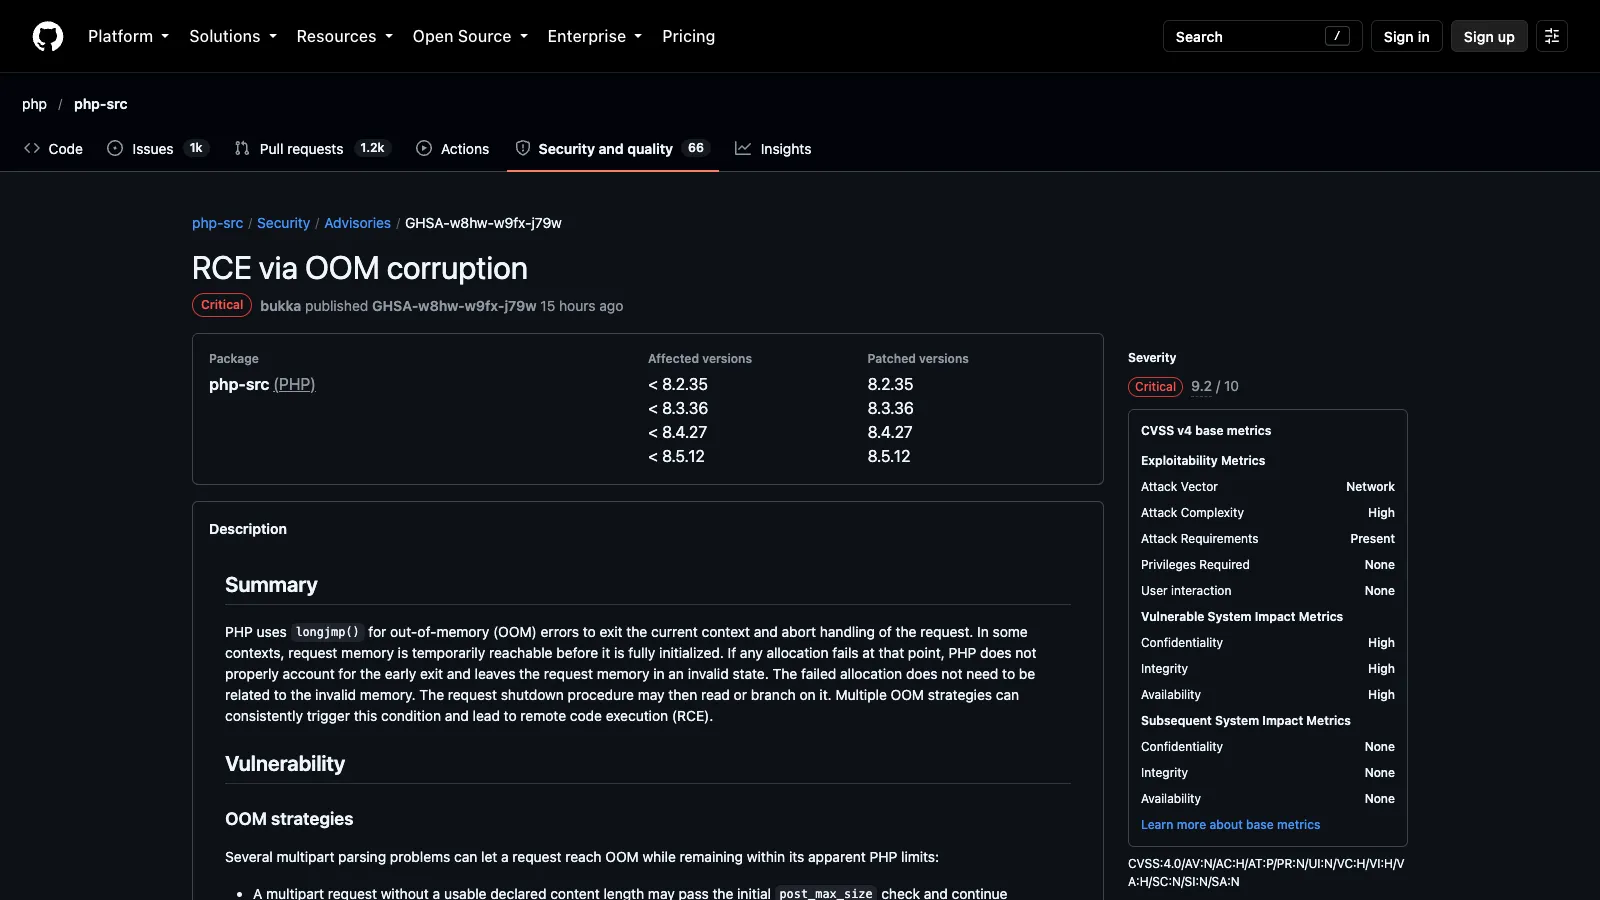
On October 21 2026 PHP released fixes for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, known together as PHP2Shell.
Meeting Room 365 doesn't use PHP in its core services. The display apps, the admin portal, and calendar sync for Microsoft 365 and Google Workspace all run on Node.js.
PHP runs in one place: isolated proxies that provide Exchange Web Services compatibility for older on-premises Exchange servers. We patched them on October 21, within hours of PHP's release. They now run PHP 8.4.27 and Ubuntu's fixed PHP 8.1 build.
Customers don't need to do anything. If your on-premises Exchange connection still uses the Proxy or Legacy proxy connection method, we do recommend upgrading it to Native, which connects to Exchange directly from our Node.js service. Change the connection method on your Exchange connection in the admin portal and press Test connection.